FH
Ferdian Hanif
CV ↗
IDENTITY // CLOUD INFRASTRUCTURE & SYSTEMS
LOC: JAKARTA · STATUS: READY FOR HIRE
CLOUD SYSTEMS ENGINEER // AWS · LINUX · IAC

Ferdian Hanif

I build and manage AWS cloud systems. I keep servers running, scale them automatically when traffic spikes, and automate routine tasks with Linux and Python.

Computer Engineering graduate from Universitas Andalas. Experienced in physical network operations at PT Semen Padang, automated AWS cloud setups, and Linux systems administration.

DEGREE: B.Eng Computer Engineering
OPS: PT Semen Padang
LOC: Jakarta, ID
50
Verified Builds
Dual-AZ
High Availability
< 3s
Event Detection

FEATURED CLOUD ARCHITECTURES // PROJECTS

FEATURED PROJECT 01 // MULTI-TIER RESILIENT CLOUD ARCHITECTURE
PRODUCTION SPEC
AWS HIGH-AVAILABILITY SYSTEM

Resilient Multi-Tier Cloud Architecture

Dual-AZ Fault-Tolerant Web and Database Topology

GOAL & SCENARIO

Keep a web application online 24/7 across two AWS data centers without single-point-of-failure risks.

HOW IT WORKS

Traffic enters through an Application Load Balancer. Compute nodes scale on demand in private subnets. The database syncs in real-time to an automatic standby replica.

RESILIENCE TEST RESULTS VERIFIED LOGS
1.
Primary DB Crash Test: Simulated a database outage. Standby replica took over in 52 seconds with zero data loss.
2.
Traffic Spike Test: Triggered 75% CPU load. Auto-scaling launched a healthy new server in 84 seconds.
FINOPS & RESOURCE EFFICIENCY < $15/MO RUNTIME

Automated off-hours shutdown scripts and right-sized instances to keep operational costs under $15 per month.

TECHNOLOGIES & TOOLS:
AWS VPC ALB EC2 Auto Scaling Amazon RDS Multi-AZ NAT Gateway CloudWatch Python Boto3 Bash
BENCHMARK: SUB-60s AUTOMATIC DB FAILOVER WITH ZERO DATA LOSS
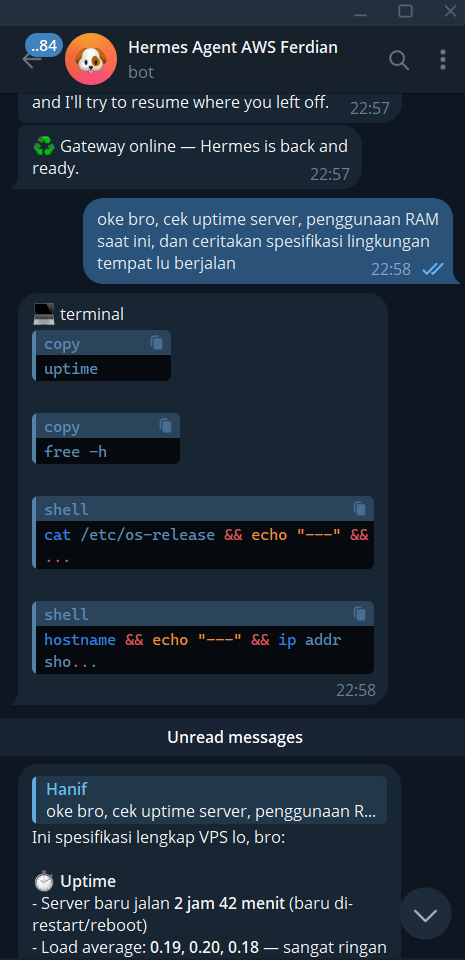
FEATURED PROJECT 02 // AUTONOMOUS AI AGENT & ZERO-TRUST GATEWAY
ZERO-TRUST & AI INFRA
AWS LIGHTSAIL & AI GATEWAY

Autonomous AI Agent on AWS Lightsail

Zero-Trust Mesh Network, Multi-LLM Gateway and Telegram Daemon

GOAL & SCENARIO

Run an autonomous AI task runner 24/7 on an inexpensive VPS without opening web ports to the public internet.

HOW IT WORKS

The AWS firewall blocks public traffic. Admin dashboards are reached via an encrypted Tailscale WireGuard mesh tunnel. Tasks are sent through Telegram using outbound HTTPS polling.

OPERATIONAL HIGHLIGHTS & TROUBLESHOOTING LIVE VERIFIED
1.
Hairpin NAT Reflection Fix: Closing external ports caused public IP calls to time out. Fixed by pointing agent traffic directly to localhost loopback 127.0.0.1.
2.
Reliability & Resource Tuning: Configured 2 GB swap to prevent OOM kernel kills. Enabled systemd user lingering to keep the agent daemon alive across reboots.
FINOPS & RUNTIME COST $12/MO FLAT PREDICTABLE

Flat $12/month Lightsail instance with 3 TB transfer. Free-tier LLM pooling via OmniRoute with automatic rate-limit fallback keeps AI inference cost at $0.

TECHNOLOGIES & TOOLS:
AWS Lightsail Ubuntu Linux Docker Tailscale WireGuard Hermes Agent OmniRoute Telegram Bot API Systemd
STATUS: 24/7 AUTONOMOUS SYSTEMD DAEMON ON AWS LIGHTSAIL
FEATURED PROJECT 03 // SERVERLESS EVENT-DRIVEN AUDIT PIPELINE
SECURITY AUTOMATION
EVENT-DRIVEN CLOUD GOVERNANCE

Serverless Security and Audit Engine

Automated Ingress Drift Detection and Rollback

THREAT SCENARIO

Opening port 22 (SSH) to 0.0.0.0/0 exposes servers to public attacks. Manual audits are too slow, so security enforcement must run in seconds.

SOLUTION

CloudTrail captures changes, EventBridge catches the event, and a Python Lambda function revokes the rule and alerts the team via SMS and email.

INCIDENT DRILL TIMELINE TOTAL: 2.85s
T+0.00s Security Group mutated (Port 22 opened to 0.0.0.0/0).
T+0.85s CloudTrail records the API management event.
T+1.40s EventBridge rule triggers Lambda function.
T+2.10s Lambda revokes unauthorized ingress rule.
T+2.85s SNS dispatches incident alert with user ID and origin IP.
TECHNOLOGIES & TOOLS:
AWS Lambda (Python) Amazon EventBridge AWS CloudTrail Amazon SNS IAM Least-Privilege Python Boto3
RESPONSE TIME: 2.85s DISCOVERY TO QUARANTINE LATENCY
TECHNICAL STACK & SYSTEMS COMPETENCIES
HANDS-ON TOOLING
STACK // CLOUD PLATFORM PRIMARY

AWS Core Infrastructure

VPC networking, compute instances, relational databases, and IAM security policies.

Amazon VPC Amazon EC2 Amazon S3 Amazon RDS Multi-AZ AWS IAM Amazon CloudWatch AWS CloudTrail Systems Manager (SSM) AWS Lambda Amazon SNS Amazon EventBridge
STACK // OPERATING SYSTEMS & NETWORKS CORE

Systems & Linux Administration

Linux server administration, automated bash scripting, and network diagnostics.

Linux (Ubuntu / Amazon Linux) Bash Shell Scripting System Hardening Patch Manager TCP/IP & Subnetting DNS / Route Tables VPC Flow Logs Fiber Optics (VFL)
STACK // AUTOMATION & PIPELINES AUTOMATION

IaC & CI/CD Automation

Declarative infrastructure as code, CI/CD automation pipelines, and cloud SDKs.

AWS CloudFormation Terraform / OpenTofu GitHub Actions CI/CD Python Boto3 SDK Git Monorepos Docker Containers REST APIs Cloud-Init Automation
STACK // DATA & HARDWARE DATA & SYSTEMS

Data & Systems Diagnostics

Database queries, structured log analytics, and physical hardware diagnostics.

PostgreSQL SQL (Athena / RDS) Python Pandas Network Cabling (RJ45/LAN) ESP32 Microcontrollers Structured Log Analytics
Foundation: Connecting physical network operations from PT Semen Padang to automated cloud infrastructure.
ALL SKILLS CODE-BACKED
AWS INFRASTRUCTURE CAPABILITY MATRIX // 50 VERIFIED BUILDS
8 DOMAINS AUDITED

AWS Infrastructure Capability Matrix

50 hands-on AWS builds covering networking, servers, databases, security, and automation. Search by keyword or filter by domain.

>_
Showing 6 of 50 builds
AWS-01 Cloud Essentials

Cloud Sandbox Environment Initialization

Baseline environment configuration and root security verification.

AWS IAM CloudShell VPC
AWS-02 Compute & OS

Amazon EC2 Web Server Lifecycle Management

Bootstrap Apache HTTP web server deployment via shell automation scripts.

Amazon EC2 Security Groups User Data
AWS-03 VPC & Networking

IP Networking & Troubleshooting Commands

Diagnostics of network latency and routing via ping, traceroute, and dig.

Linux CLI TCP/IP DNS
AWS-04 VPC & Networking

Public & Private IP Address Diagnostics

Network addressing verification and private subnet segmentation.

Amazon VPC CIDR Subnets
AWS-05 VPC & Networking

Static and Dynamic Elastic IP Architecture

Configuring static public IPv4 persistence across instance lifecycle restarts.

Amazon EC2 Elastic IP DNS
AWS-06 VPC & Networking

L3/L4 Network Issue Troubleshooting

Root cause analysis of dropped packets across route tables and security filters.

Route Tables Security Groups NACL
Showing 6 featured builds