FH
Ferdian Hanif
CV ↗
IDENTITY // CLOUD INFRASTRUCTURE & SYSTEMS
LOC: JAKARTA · STATUS: READY FOR HIRE
CLOUD SYSTEMS ENGINEER // AWS · LINUX · IAC

Ferdian Hanif

I build and manage AWS cloud systems. I keep servers running, scale them automatically when traffic spikes, and automate routine tasks with Linux and Python.

Computer Engineering graduate from Universitas Andalas (GPA 3.32). Experienced in physical network operations at PT Semen Padang, automated AWS cloud setups, and Linux systems administration.

DEGREE: B.Eng Computer Eng (3.32)
OPS: PT Semen Padang
LOC: Jakarta, ID
cloud-shell // aws-cli
> aws sts get-caller-identity

{

"UserId": "AROA49J87V7EXAMPLE:ferdian",

"Account": "VERIFIED_ENGINEER",

"Arn": "arn:aws:iam::cloud:role/InfrastructureEngineer"

}

> aws cloudformation describe-stacks --query "Stacks[].StackStatus"

[ "CREATE_COMPLETE", "UPDATE_COMPLETE" ]

REGION: ap-southeast-1 (Singapore) MFA ENFORCED
50
Verified Builds
Dual-AZ
High Availability
< 3s
Event Detection

FEATURED CLOUD ARCHITECTURES // PROJECTS

FEATURED PROJECT 01 // MULTI-TIER RESILIENT CLOUD ARCHITECTURE
PRODUCTION SPEC
AWS HIGH-AVAILABILITY SYSTEM

Resilient Multi-Tier Cloud Architecture

Dual-AZ Fault-Tolerant Web and Database Topology

GOAL & SCENARIO

Keep a web application online 24/7 across two AWS data centers without single-point-of-failure risks.

HOW IT WORKS

Traffic enters through an Application Load Balancer. Compute nodes scale on demand in private subnets. The database syncs in real-time to an automatic standby replica.

RESILIENCE TEST RESULTS VERIFIED LOGS
1.
Primary DB Crash Test: Simulated a database outage. Standby replica took over in 52 seconds with zero data loss.
2.
Traffic Spike Test: Triggered 75% CPU load. Auto-scaling launched a healthy new server in 84 seconds.
FINOPS & RESOURCE EFFICIENCY < $15/MO RUNTIME

Automated off-hours shutdown scripts and right-sized instances to keep operational costs under $15 per month.

TECHNOLOGIES & TOOLS:
AWS VPC ALB EC2 Auto Scaling Amazon RDS Multi-AZ NAT Gateway CloudWatch Python Boto3 Bash
TOPOLOGY // DUAL-AZ VPC INFRASTRUCTURE ap-southeast-1
VPC 10.0.0.0/16 (2 AZs) INTERNET GATEWAY / ALB AZ-1A (ap-southeast-1a) AZ-1B (ap-southeast-1b) PUBLIC SUBNET (NAT GW) NAT-GW-A PUBLIC SUBNET (STANDBY) ROUTER / IGW APP TIER // AUTO SCALING EC2 EC2-NODE-01 APP TIER // AUTO SCALING EC2 EC2-NODE-02 DB TIER (ISOLATED) RDS PRIMARY (ACTIVE) MariaDB Multi-AZ DB TIER (ISOLATED) RDS STANDBY (SYNC) Auto-Failover Replica SYNC REPL
Active Compute Node
Primary Multi-AZ DB
BENCHMARK: SUB-60s AUTOMATIC DB FAILOVER WITH ZERO DATA LOSS
FEATURED PROJECT 02 // AUTONOMOUS AI AGENT & ZERO-TRUST GATEWAY
ZERO-TRUST & AI INFRA
AWS LIGHTSAIL & AI GATEWAY

Autonomous AI Agent on AWS Lightsail

Zero-Trust Mesh Network, Multi-LLM Gateway and Telegram Daemon

GOAL & SCENARIO

Run an autonomous AI task runner 24/7 on an inexpensive VPS without opening web ports to the public internet.

HOW IT WORKS

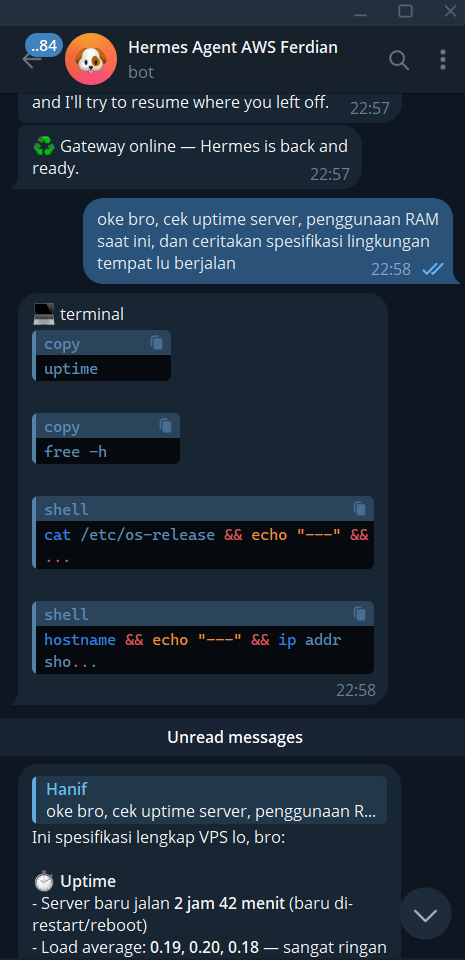
The AWS firewall blocks public traffic. Admin dashboards are reached via an encrypted Tailscale WireGuard mesh tunnel. Tasks are sent through Telegram using outbound HTTPS polling.

OPERATIONAL HIGHLIGHTS & TROUBLESHOOTING LIVE VERIFIED
1.
Hairpin NAT Reflection Fix: Closing external ports caused public IP calls to time out. Fixed by pointing agent traffic directly to localhost loopback 127.0.0.1.
2.
Reliability & Resource Tuning: Configured 2 GB swap to prevent OOM kernel kills. Enabled systemd user lingering to keep the agent daemon alive across reboots.
FINOPS & RUNTIME COST $12/MO FLAT PREDICTABLE

Flat $12/month Lightsail instance with 3 TB transfer. Free-tier LLM pooling via OmniRoute with automatic rate-limit fallback keeps AI inference cost at $0.

TECHNOLOGIES & TOOLS:
AWS Lightsail Ubuntu Linux Docker Tailscale WireGuard Hermes Agent OmniRoute Telegram Bot API Systemd
TOPOLOGY // ZERO-TRUST AI ARCHITECTURE
ADMIN WORKSTATION Laptop / Mobile Device Tailscale: 100.116.x.x TELEGRAM USER Mobile / Desktop App Task Prompts / Shell HTTPS 443 POLLING AWS LIGHTSAIL VPS (Jakarta ap-southeast-3a) FIREWALL: PORT 22 (SSH) ONLY // PORTS 20128 & 9119 BLOCKED HERMES AGENT Systemd User Linger Daemon (~150MB RAM) Autonomous Execution 127.0.0.1:20128/v1 Loopback Fix OMNIROUTE GATEWAY Docker (Host Network) Port 20128: tailscale0 Rate-Limit Auto Fallback Zero-Trust Admin Access RESOURCE GOVERNANCE & FINOPS 2 GB Swap (Anti-OOM Buffer) | $12/mo Flat Lightsail | $0 Inference Cost LLM PROVIDERS Outbound API Google Gemini Primary Model Groq (Llama 3.3) Low-Latency Fallback OpenCode / CF Secondary Standby HTTP 429 Retry Automatic Routing
Tailscale WireGuard Mesh Tunnel
Hermes Autonomous Agent Daemon
STATUS: 24/7 AUTONOMOUS SYSTEMD DAEMON ON AWS LIGHTSAIL
FEATURED PROJECT 03 // SERVERLESS EVENT-DRIVEN AUDIT PIPELINE
SECURITY AUTOMATION
EVENT-DRIVEN CLOUD GOVERNANCE

Serverless Security and Audit Engine

Automated Ingress Drift Detection and Rollback

THREAT SCENARIO

Opening port 22 (SSH) to 0.0.0.0/0 exposes servers to public attacks. Manual audits are too slow, so security enforcement must run in seconds.

SOLUTION

CloudTrail captures changes, EventBridge catches the event, and a Python Lambda function revokes the rule and alerts the team via SMS and email.

INCIDENT DRILL TIMELINE TOTAL: 2.85s
T+0.00s Security Group mutated (Port 22 opened to 0.0.0.0/0).
T+0.85s CloudTrail records the API management event.
T+1.40s EventBridge rule triggers Lambda function.
T+2.10s Lambda revokes unauthorized ingress rule.
T+2.85s SNS dispatches incident alert with user ID and origin IP.
TECHNOLOGIES & TOOLS:
AWS Lambda (Python) Amazon EventBridge AWS CloudTrail Amazon SNS IAM Least-Privilege Python Boto3
EVENT FLOW // DRIFT DETECTION PIPELINE EVENT-DRIVEN
MUTATION EVENT AuthorizeSecurity- GroupIngress (0.0.0.0/0) CLOUDTRAIL / EVENTBRIDGE Rule: Pattern Match detail.eventName AWS LAMBDA Python 3.11 Runtime Parse SG IP Perms < 300ms Exec ACTION A: ROLLBACK revoke_security_group_ingress Automatic removal of open CIDR 0.0.0.0/0 on Port 22 ACTION B: SNS ALERT Topic: SecurityAlerts Immediate notification with IAM user and origin IP
Event Ingestion & Alerting
Lambda Execution Engine
RESPONSE TIME: 2.85s DISCOVERY TO QUARANTINE LATENCY
TECHNICAL STACK & SYSTEMS COMPETENCIES
HANDS-ON TOOLING
STACK // CLOUD PLATFORM PRIMARY

AWS Core Infrastructure

VPC networking, compute instances, relational databases, and IAM security policies.

Amazon VPC Amazon EC2 Amazon S3 Amazon RDS Multi-AZ AWS IAM Amazon CloudWatch AWS CloudTrail Systems Manager (SSM) AWS Lambda Amazon SNS Amazon EventBridge
STACK // OPERATING SYSTEMS & NETWORKS CORE

Systems & Linux Administration

Linux server administration, automated bash scripting, and network diagnostics.

Linux (Ubuntu / Amazon Linux) Bash Shell Scripting System Hardening Patch Manager TCP/IP & Subnetting DNS / Route Tables VPC Flow Logs Fiber Optics (VFL)
STACK // AUTOMATION & PIPELINES AUTOMATION

IaC & CI/CD Automation

Declarative infrastructure as code, CI/CD automation pipelines, and cloud SDKs.

AWS CloudFormation Terraform / OpenTofu GitHub Actions CI/CD Python Boto3 SDK Git Monorepos Docker Containers REST APIs Cloud-Init Automation
STACK // DATA & HARDWARE DATA & SYSTEMS

Data & Systems Diagnostics

Database queries, structured log analytics, and physical hardware diagnostics.

PostgreSQL SQL (Athena / RDS) Python Pandas Network Cabling (RJ45/LAN) ESP32 Microcontrollers Structured Log Analytics
Foundation: Connecting physical network operations from PT Semen Padang to automated cloud infrastructure.
ALL SKILLS CODE-BACKED
AWS INFRASTRUCTURE CAPABILITY MATRIX // 50 VERIFIED BUILDS
8 DOMAINS AUDITED

AWS Infrastructure Capability Matrix

50 hands-on AWS builds covering networking, servers, databases, security, and automation. Search by keyword or filter by domain.

>_
Showing 50 of 50 builds
AWS-01 Cloud Essentials

Cloud Sandbox Environment Initialization

Baseline environment configuration and root security verification.

AWS IAM CloudShell VPC
AWS-02 Compute & OS

Amazon EC2 Web Server Lifecycle Management

Bootstrap Apache HTTP web server deployment via shell automation scripts.

Amazon EC2 Security Groups User Data
AWS-03 VPC & Networking

IP Networking & Troubleshooting Commands

Diagnostics of network latency and routing via ping, traceroute, and dig.

Linux CLI TCP/IP DNS
AWS-04 VPC & Networking

Public & Private IP Address Diagnostics

Network addressing verification and private subnet segmentation.

Amazon VPC CIDR Subnets
AWS-05 VPC & Networking

Static and Dynamic Elastic IP Architecture

Configuring static public IPv4 persistence across instance lifecycle restarts.

Amazon EC2 Elastic IP DNS
AWS-06 VPC & Networking

L3/L4 Network Issue Troubleshooting

Root cause analysis of dropped packets across route tables and security filters.

Route Tables Security Groups NACL
AWS-07 VPC & Networking

Subnet Architecture in Amazon VPC

Designing dual-AZ isolated public and private subnet topologies.

Amazon VPC Subnets Availability Zones
AWS-08 VPC & Networking

VPC Gateway & Routing Infrastructure

Orchestrating internet breakout for compute instances in public subnets.

Internet Gateway Route Tables VPC
AWS-09 VPC & Networking

End-to-End VPC Build & Production Web Server

End-to-end custom VPC construction hosting a live production web service.

Amazon VPC Amazon EC2 Security Groups
AWS-10 Database & Data

Database Schema & Table Operations

Structured relational schema definitions and table partitioning.

Relational DB SQL DDL
AWS-11 Database & Data

Transactional DML Database Operations

Optimized INSERT, UPDATE, and DELETE operations under transactional integrity.

SQL DML ACID Compliance
AWS-12 Database & Data

Complex Query Formulation & Optimization

Performance-tuned JOIN operations and high-volume data selection.

SQL DQL Query Optimization
AWS-13 Database & Data

Conditional Data Filtering & Indexing

High-efficiency WHERE predicate filtering and compound index usage.

SQL Filtering Data Indexing
AWS-14 Database & Data

Aggregate Functions & Analytics Processing

Statistical transformation and window functions for analytical reporting.

SQL Analytics Aggregations
AWS-15 Database & Data

Data Organization & Grouping Strategies

Multi-dimensional categorical groupings and summarized dataset generation.

SQL Grouping HAVING Filters
AWS-16 Database & Data

Database Server Build & Application Integration

Decoupling application tier compute from managed relational database tier.

Amazon RDS PHP Application EC2
AWS-17 Database & Data

Amazon Aurora Distributed Database Cluster

Deploying high-performance fault-tolerant Aurora storage clusters.

Amazon Aurora Storage Engine Read Replicas
AWS-18 Database & Data

Amazon DynamoDB NoSQL Low-Latency Storage

Single-digit millisecond query performance with global partition key schema.

Amazon DynamoDB NoSQL Partition Keys
AWS-19 Database & Data

Challenge: Autonomous Database Tier Deployment

Zero-guidance challenge provisioning relational backend tied to dynamic frontend.

Amazon RDS CLI Automation Security Groups
AWS-20 Security & Governance

Systems Hardening via AWS Systems Manager Patch Manager

Automated fleet OS patching and vulnerability remediation without SSH.

AWS Systems Manager Patch Baselines Linux
AWS-21 Security & Governance

Data-at-Rest & In-Transit Encryption via AWS KMS

Envelope encryption implementation and cryptographic key rotation policies.

AWS KMS Customer Managed Keys EBS Encryption
AWS-22 Security & Governance

Enterprise Identity & Access Management (IAM)

Fine-grained least-privilege policy authoring and role delegation.

AWS IAM RBAC Least Privilege
AWS-23 Security & Governance

Malware Protection via AWS Network Firewall

Stateful packet inspection and domain filtering to prevent outbound exfiltration.

AWS Network Firewall Suricata Rules VPC
AWS-24 Observability & Monitoring

Compute Health Monitoring & CloudWatch Alarms

Automated alarm triggers and email notification dispatches on CPU threshold breach.

Amazon CloudWatch Amazon SNS Amazon EC2
AWS-25 IaC & Automation

AWS CLI Tooling Automation & Credential Security

Programmatic cloud infrastructure management with secured credential profiles.

AWS CLI IAM Credentials Bash
AWS-26 Compute & OS

Fleet Management via SSM Run Command & Session Manager

Secure bastionless shell access and bulk script execution across instances.

AWS Systems Manager Session Manager IAM
AWS-27 Storage & DR

Amazon S3 Static Website & CLI Sync Pipelines

Static content delivery with granular public read bucket policies.

Amazon S3 AWS CLI Bucket Policies
AWS-28 Compute & OS

Automated EC2 Provisioning via AWS CLI Automation

Scripted deployment of customized compute instances with automated tags.

Amazon EC2 AWS CLI Shell Scripting
AWS-29 Compute & OS

Challenge: Autonomous EC2 Instance Exercise

Autonomous specification matching and isolated compute node provisioning.

Amazon EC2 Security Groups Linux CLI
AWS-30 Compute & OS

Instance Creation Troubleshooting & RCA

Diagnosing failure modes across AMI architectural mismatches and quotas.

Amazon EC2 AMI Instance Types
AWS-31 Compute & High Availability

Scale & Load Balance Multi-Tier Architecture

Traffic distribution across dual Availability Zones via Application Load Balancer.

Application Load Balancer Target Groups EC2
AWS-32 Compute & High Availability

Dynamic EC2 Auto Scaling Under Workload Spikes

Automated horizontal scaling elasticity based on real-time metric thresholds.

Auto Scaling Groups CloudWatch Launch Templates
AWS-33 VPC & Networking

Amazon Route 53 Health Checks & Failover Routing

Automated DNS failover routing directing traffic away from impaired origins.

Amazon Route 53 DNS Failover Health Checks
AWS-34 Serverless & Compute

Event-Driven Serverless Compute via AWS Lambda

Stateless serverless function execution triggered by Amazon S3 object events.

AWS Lambda Python CloudWatch Logs
AWS-35 Serverless & Compute

Challenge: Autonomous Serverless Lambda Orchestration

Autonomous build of event-driven image processing functions without servers.

AWS Lambda IAM Roles Python
AWS-36 Database & Data

Live Database Migration to Amazon RDS for MariaDB

Zero-data-loss relational database export/import migration to managed RDS.

Amazon RDS MariaDB mysqldump
AWS-37 VPC & Networking

Complex Multi-Tier Amazon VPC Configuration

Enterprise network topology with isolated private database subnets and NAT.

Amazon VPC NAT Gateway Route Tables
AWS-38 Storage & DR

Storage Lifecycle Automation & S3 Versioning DR

Cron-scheduled automated EBS snapshot lifecycle pruning and S3 object recovery.

Amazon S3 Amazon EBS Python Boto3
AWS-39 VPC & Networking

VPC Flow Logs Forensic Analysis & L3/L4 Network Triage

Forensic log analysis resolving L3 default route outages and L4 NACL blocks.

VPC Flow Logs Amazon Athena Security Groups
AWS-40 Storage & DR

Amazon EBS Block Storage & Disaster Recovery

Volume formatting, fstab persistence, snapshotting, and point-in-time DR restoration.

Amazon EBS EBS Snapshots Linux fstab
AWS-41 Storage & DR

Amazon S3 Event Notifications & IAM Prefix Delegation

Event notifications wired to SNS with prefix-level IAM access segregation.

Amazon S3 Amazon SNS IAM Policies
AWS-42 Storage & DR

Challenge: Granular Object ACL Security & Public Hosting

Decoupling bucket-level BPA to enforce object-level ACL public reads.

Amazon S3 S3 Block Public Access AWS CLI
AWS-43 Observability & Monitoring

Enterprise Observability with CloudWatch Agent & AWS Config

SSM-deployed CloudWatch agents, log filter alarms, and AWS Config compliance rules.

CloudWatch Agent EventBridge AWS Config
AWS-44 Security & Governance

CloudTrail Multi-Region Audit & Athena Security Forensics

Forensic triage identifying rogue IAM threat actors and remediating attack vectors.

AWS CloudTrail Amazon Athena AWS KMS
AWS-45 IaC & Automation

FinOps Resource Governance with Tagging & The Stopinator

Dynamic compute discovery, automated off-hours shutdown, and tag enforcement.

AWS CLI JMESPath Boto3/PHP SDK FinOps
AWS-46 IaC & Automation

Rightsizing Compute Optimization & TCO Modeling

Monolith database decoupling and vertical compute rightsizing cutting costs by 50%.

AWS CLI Amazon RDS AWS Pricing Calculator
AWS-47 IaC & Automation

Declarative Infrastructure as Code with AWS CloudFormation

Automated multi-tier stack deployment using YAML templates and dynamic parameters.

AWS CloudFormation SSM Parameter Store S3
AWS-48 IaC & Automation

CloudFormation Deployment Troubleshooting & Drift Detection

Root cause analysis on cloud-init failure logs, stack drift audit, and retain teardown.

AWS CloudFormation Drift Detection cloud-init
AWS-49 IaC & Automation

Challenge: Autonomous CloudFormation Isolated VPC & Compute

Autonomous authoring of production YAML stacks with private subnet compute nodes.

AWS CloudFormation Amazon VPC EC2
AWS-50 Machine Learning & AI

Amazon SageMaker Machine Learning Container Pipeline

Data partitioning, containerized model training, and artifact storage on S3.

Amazon SageMaker XGBoost Amazon S3